Okta's AI Agent Gateway Brings Runtime Governance to Enterprise AI Agents
Published by AINave Editorial • Reviewed by Ramit
Okta used the opening day of its Oktane conference to announce a runtime enforcement layer for AI agents called Agent Gateway, along with a multi-vendor security framework called the Blueprint Alliance. The message is clear: enterprise AI agent governance is moving from post-hoc logging to real-time enforcement, and no single vendor plans to solve it alone.
Real-time policy enforcement on the execution path
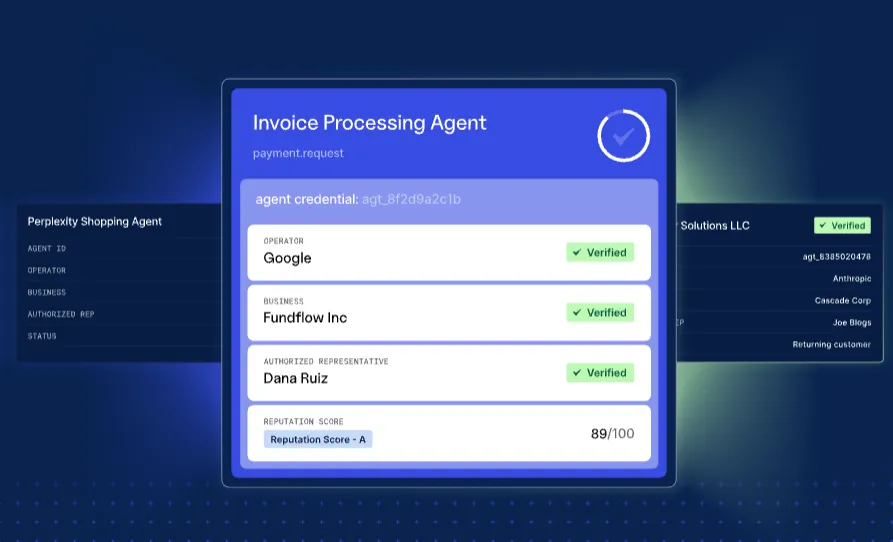
Agent Gateway sits between an AI agent and the tools it calls, enforcing policy and logging each interaction as it happens. Okta's previous approach relied on capturing agent events in its System Log for review after the fact. The gateway shifts that to runtime, where it brokers credentials at every tool call and requires no code changes to the agent itself. When an agent routed through the gateway is deactivated, Okta plans to revoke every active token and terminate every session in flight, effectively a kill switch for agent execution.
Discovery and identity for every agent
Shadow AI Agent Discovery for Endpoints extends agent discovery to employee laptops and desktops, catching unmanaged agents that escape browser-based detection. Okta already supports importing known agents from Amazon Bedrock and Salesforce Agentforce. Once discovered, Agent SSO brings Cross App Access to all SSO customers, replacing long-lived keys with short-lived tokens tied to an identity. Agent-to-Agent Connections codify which agents may call which others, with each handoff recorded in an auditable chain. Resource Access Certifications review standing permissions over time, and Configuration Designer draws the entire agent-to-resource map visually.
The Blueprint Alliance: Open standards across vendors
Okta co-founded the Blueprint Alliance with 11 other vendors, including AWS, CrowdStrike, Google Cloud, Databricks, Docker, Lovable, Proofpoint, Salesforce, ServiceNow, Wiz, and Zscaler. The alliance rewrites Okta's March security framework into an open, multivendor reference architecture. Members have agreed to treat every agent as a first-class identity and to scope its access to the task at hand. The framework adds containment through token revocation, session termination, or network quarantine, with a staged, auditable path for restoring a compromised agent. Members are already testing interoperability across MCP, the Open Cybersecurity Schema Framework, and the Shared Signals Framework, aiming for a threat signal from one member's monitor to trigger action across every connected control plane.
What this means for builders
For teams deploying AI agents in enterprise environments, Okta's runtime governance changes the operational risk profile. The ability to revoke tokens and kill sessions at runtime means an agent compromise no longer has to cascade across toolchains. Short-lived tokens reduce the blast radius of leaked credentials. And the auditable chain of agent-to-agent handoffs provides a clear trail for post-incident analysis. The no-code integration point with Agent Gateway lowers the barrier for existing deployments. However, the kill switch and gateway are not yet generally available: they are planned for the third quarter of 2026, with the full kill switch and Configuration Designer coming in Q4.
The Blueprint Alliance's open standards approach matters for builders who need to avoid lock-in. If threat signals can span Okta, CrowdStrike, and AWS control planes, an agent running on Bedrock could be shut down by an Okta identity trigger. That level of interoperability remains aspirational until joint test results are published, but the founding members and principles signal serious intent.
Gartner research cited by the alliance predicts that the average Fortune 500 enterprise will have more than 150,000 agents in use by 2028, yet only 13% of organizations think they have the right governance in place. Okta's announcements are a direct response to that gap, but the proof will be in how well the gateway and alliance interoperate across real enterprise environments.
FAQs
Sources
- Okta adds AI agent runtime gateway, forms Blueprint Alliance with AWS and CrowdStrike - SiliconANGLE
- Industry leaders form the Blueprint Alliance to advance a shared...
- Amanda Adams, CrowdStrike & Mona Chadha, AWS - YouTube
- CrowdStrike Extends Falcon Platform Capabilities Across Google...
- Home | Runtime
- Okta Wants Identity to Be the Control Plane for AI Agents
- CrowdStrike and Okta Soar as AI Could Create “About 90” New Identities Per Worker
- CrowdStrike Unveils Falcon Guardian to Secure AI Agents Where They Execute: On the Endpoint at Runtime
- AWS Marketplace: CrowdStrike
- Herdr: the runtime coding agents run on
- Okta adds AI agent runtime gateway, forms... - aVenture News
- Okta adds AI agent runtime… — AI Startups | OnAirToday
- Okta Launches AI Agent Gateway, Forms 12-Vendor Alliance
- Okta Agent Gateway: Secure Runtime AI Agent Governance
- Okta (OKTA) Launches Agent SSO For Enterprise AI Access